Cyber threat intelligence platform
Know what the dark web knows about you.
Dark web and ransomware intelligence for Indian enterprises. Analyst‑verified. Scoped to you.
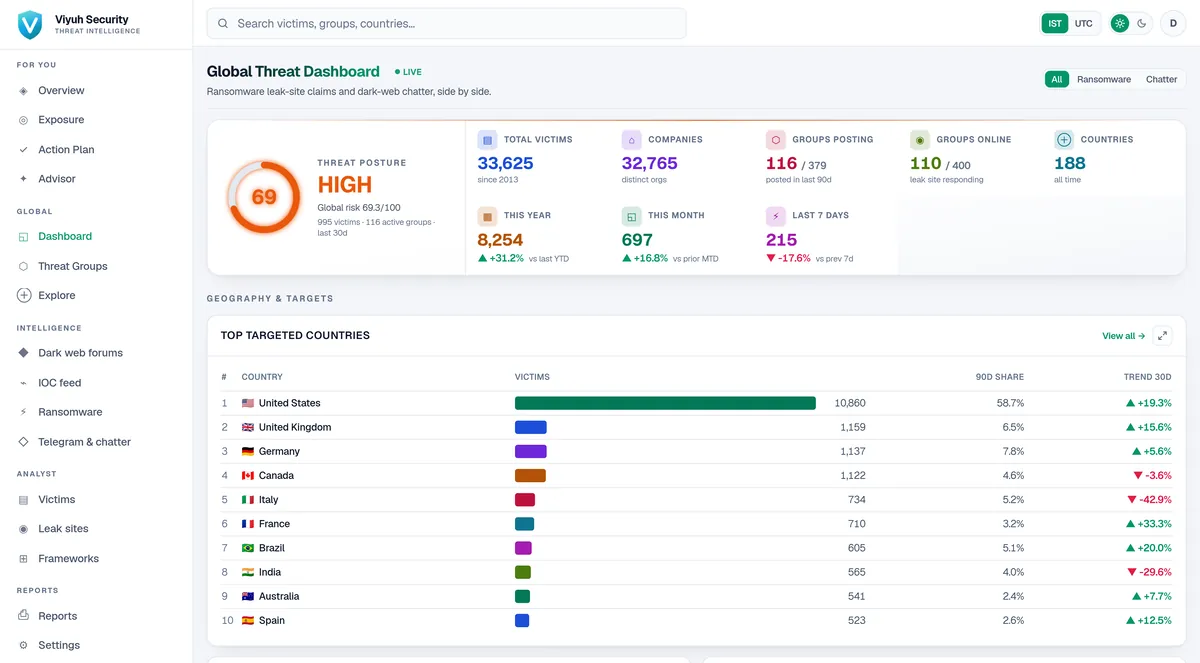
- Ransomware victims tracked across 188 countries
- 33,000+
- Ransomware families
- 542
- Proprietary breach data
- 7 TB+
The problem
Most threat intelligence goes unread.
Generic feeds cover the whole internet and say little about you. Half of security teams can't tell if their intel is credible.
Viyuh gives you both: the global picture and exactly where you sit in it. Every finding is checked by an analyst before you act on it.
Why Viyuh
The global picture, ranked for you.
-
01
Analyst-verified
Every IOC is hand-checked. Leak claims are tested for legitimacy. Verified findings are marked, so you act on those first.
-
02
Scoped to you
Everything we collect is ranked against your sector, geography, domains and software. Our ML model labels the 1 in 4 victims posted without an industry, so those attacks still reach you.
-
03
Plugs into your SOC
STIX/TAXII into your SIEM, SOAR or firewall. Real-time alerts on the dashboard and by email. Full API.
-
04
Built for India
Mapped to the DPDP Act, NIST CSF 2.0, NIST SP 800-53, ISO 27001 and SOC 2. Data hosted in India.
Intelligence-led services
The team watching attackers is the team that answers your call.
Most threat intelligence vendors stop at the alert. Most responders start without it. Viyuh does both under one roof. Each side sharpens the other.
-
01
Monitoring where stolen data is sold
Ransomware leak sites, dark web forums, Telegram and breach data, watched for your domains, brands and people. Analyst-verified alerts, by email and into your SIEM.
-
02
Incident response that checks the dark web from hour one
Is your stolen data already posted or for sale? We look from the first hour, alongside containment.
-
03
Forensics backed by our own breach data
Investigations can draw on our breach corpus and dark web collection. Evidence is handled for internal inquiries and court.
Services
From the first alert to the courtroom.
-
01
Incident response, 24/7
Containment, ransomware response and forensic investigation. Response in under 15 minutes. Support with CERT-In 6-hour incident reporting.
Scope and deliverables: Incident response -
02
Digital forensics and investigations
Insider threat, fraud, data theft and business email compromise. Court-admissible evidence handling.
Scope and deliverables: Forensics -
03
Dark web monitoring and threat intelligence
Ransomware tracking, credential exposure and Telegram monitoring. Delivered through our platform.
Scope and deliverables: Threat intelligence
Coverage
Built on our own collection.
A live dataset. Ransomware victims in 188 countries, tracked since 2013. Our analysts watch dark web and deep web activity around the clock, so these numbers grow every week. Figures as of October 2026.
- Ransomware victims since 2013
- 33,000+
- Ransomware families
- 542
- Dark web links tracked
- 5,700+
- Forum and Telegram posts
- 52,000+
- Breach data
- 7 TB+
- Exploited CVEs scored
- 1,700+
- MITRE ATT&CK techniques
- 358
- Indian victims
- 560+
About
The people behind the intelligence also clean up after attacks.
Viyuh Security is a cyber security firm based in Delhi NCR. The team behind the platform also responds to incidents and investigates breaches. So our intelligence reflects how attacks really unfold.
Request a demo
See your own threat picture, live.
Book a demo of the platform or talk to an expert about an engagement. Under attack? Call our 24/7 line.