The platform
Everything aimed at you, in one view.
Ransomware leak sites, dark web forums, Telegram channels and breach data, collected around the clock and turned into one live picture of the threat. Analyst‑verified. Hosted in India.
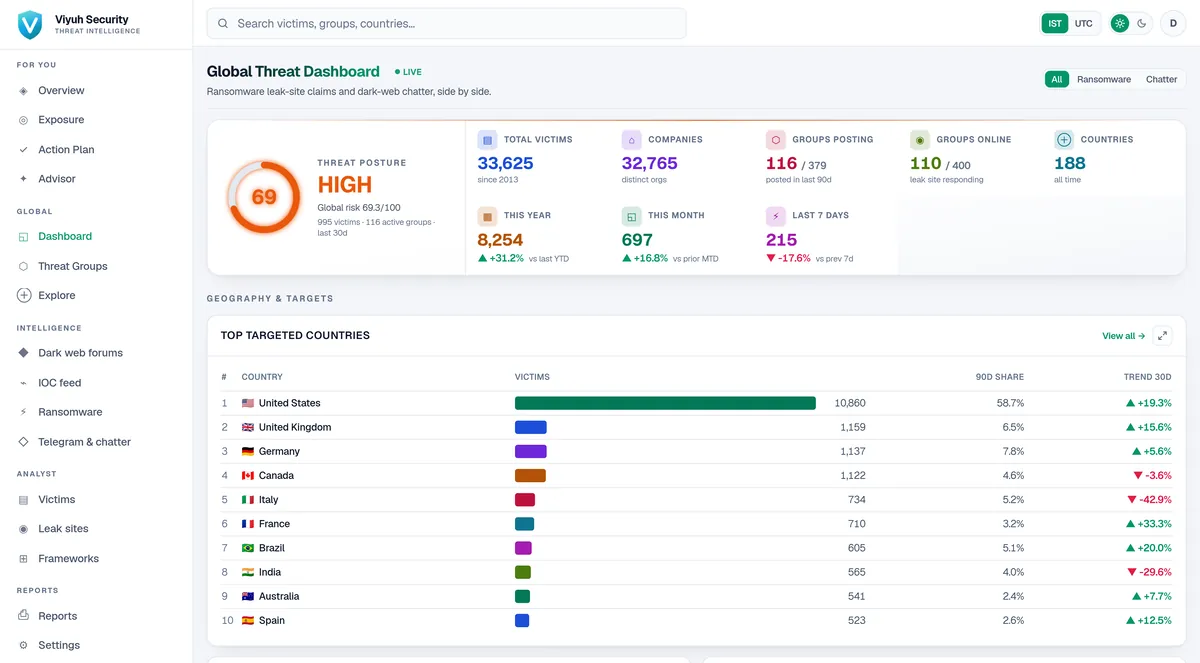
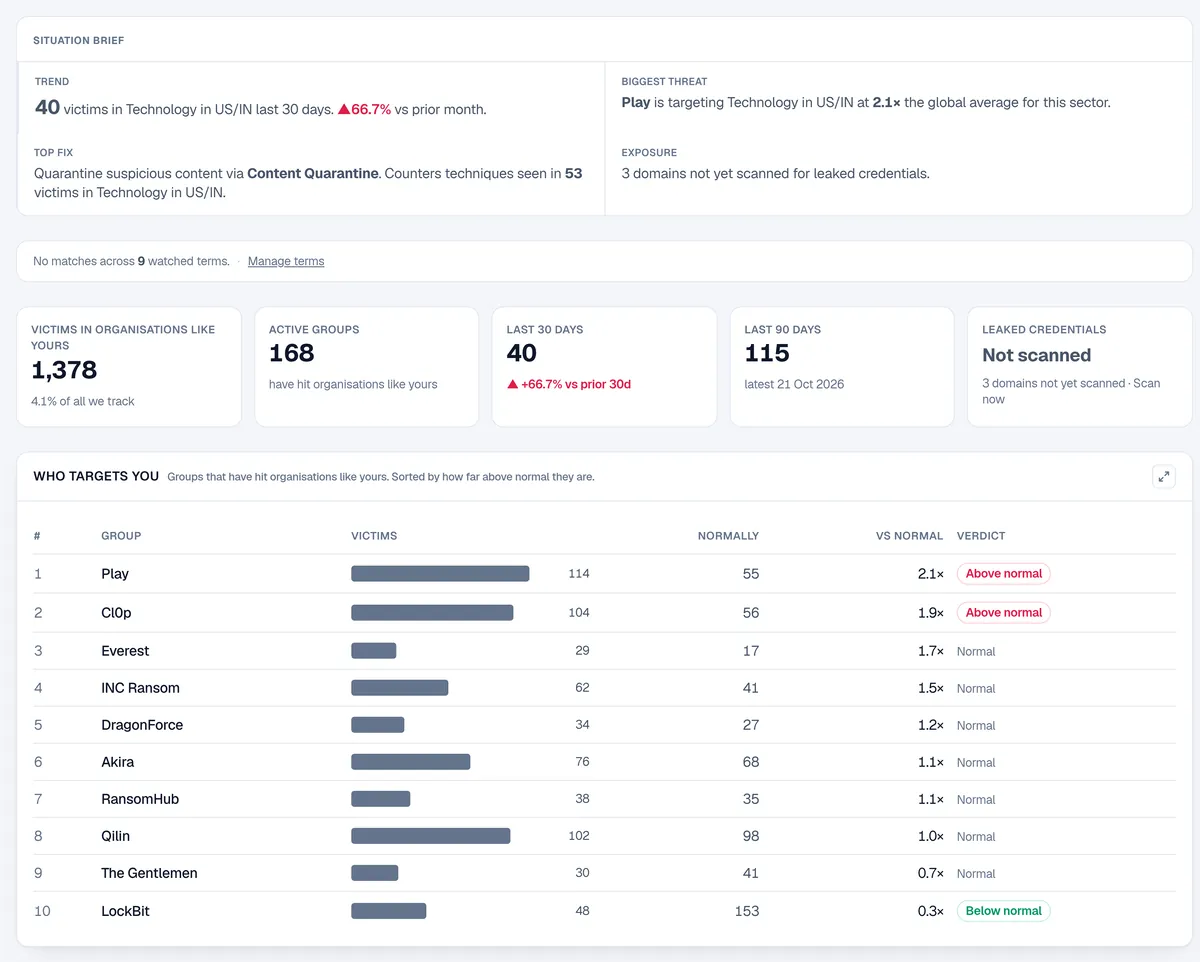
Two views, one toggle
The whole threat picture, and exactly where you sit in it.
The global view is always there: the full dataset across every sector and region.
Your own view is set up once and becomes your landing page. It opens on a situation brief, the groups hitting organisations like yours ranked by how far above normal they are, and the top fix to make first. One toggle switches between the two.
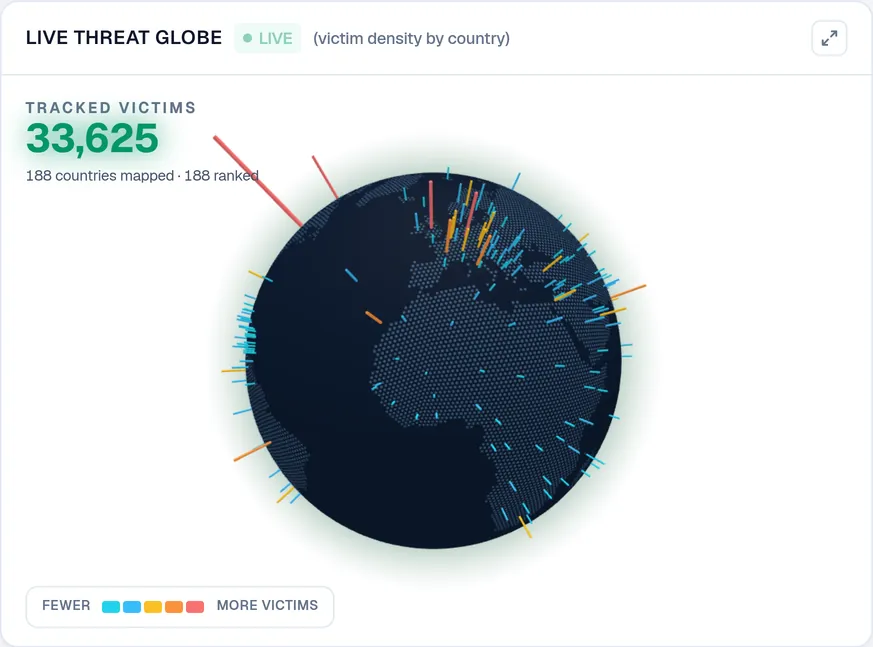
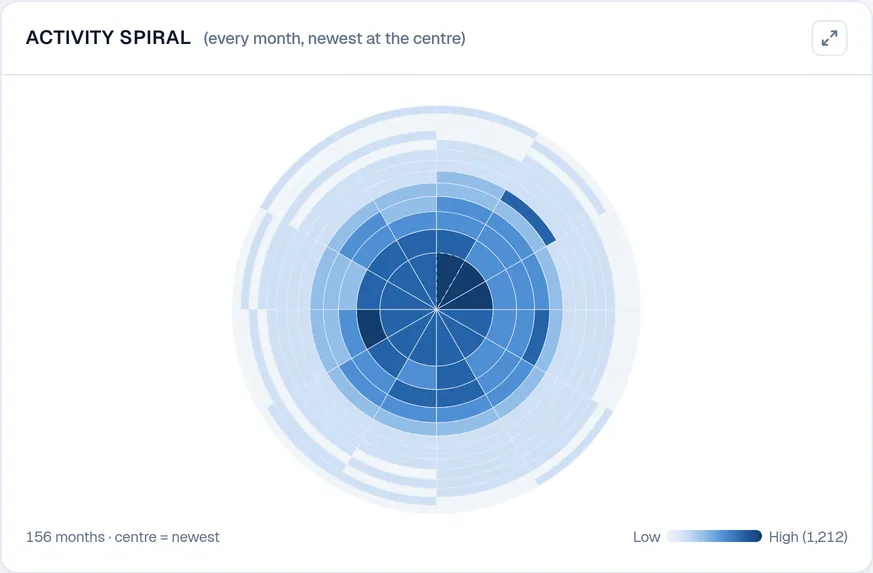
Visual intelligence
Every angle on the threat, from one dataset.
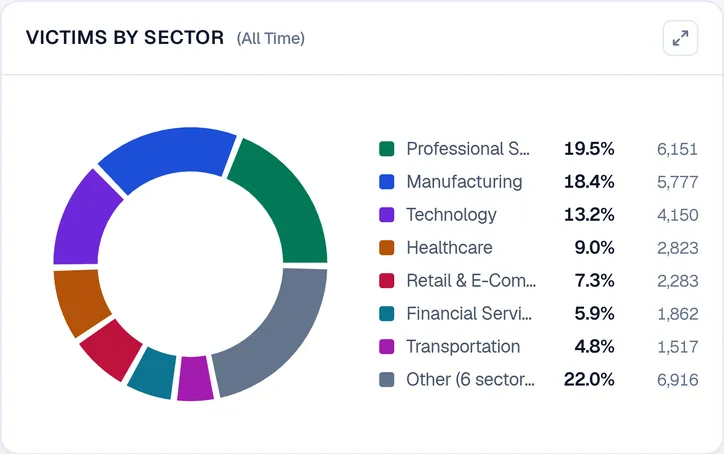
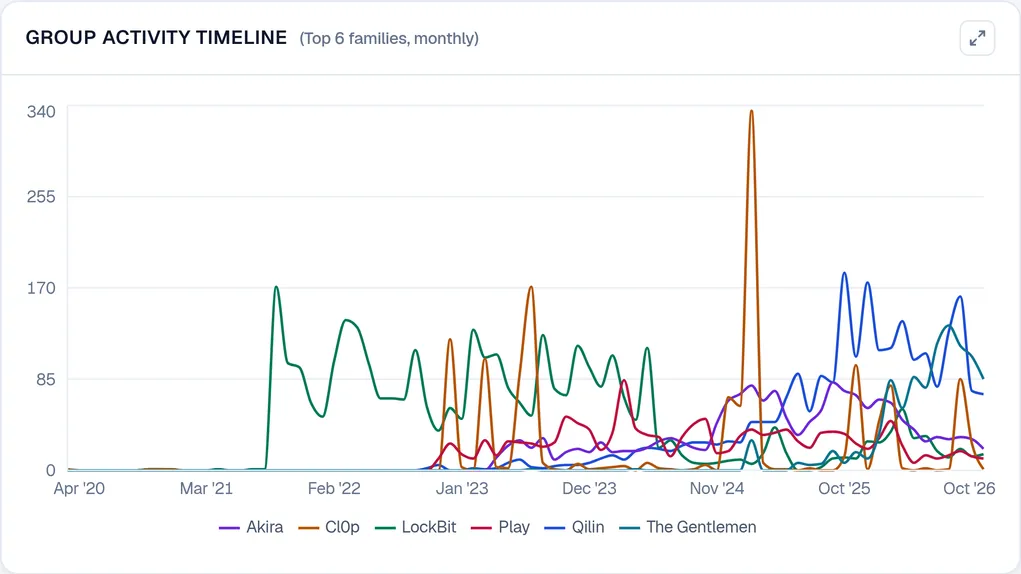
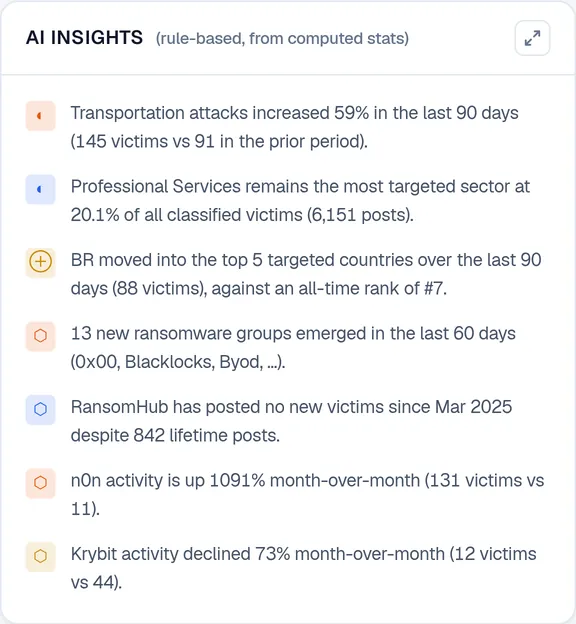
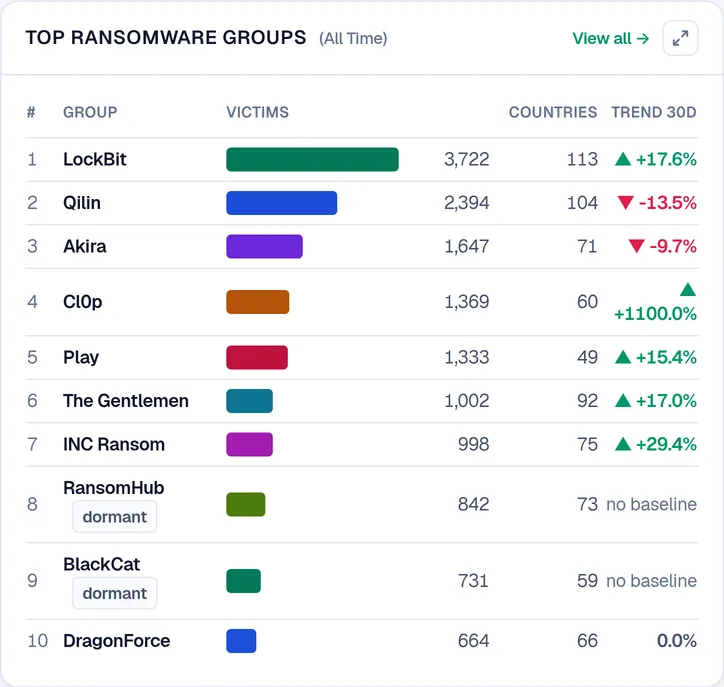
Live maps, forecasts and heatmaps built on our own collection. Read the global picture in seconds, then drill into what concerns you.
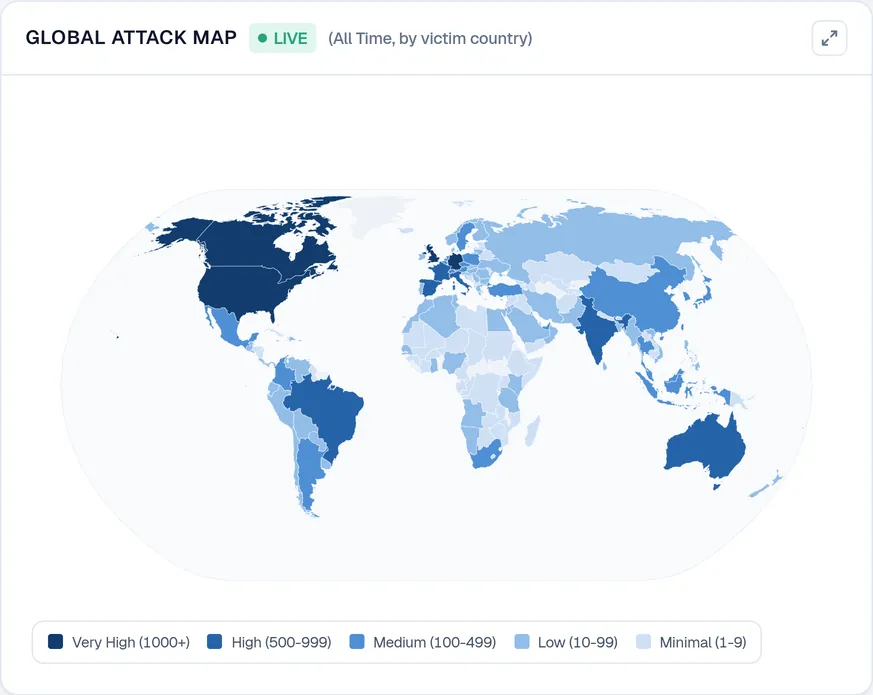
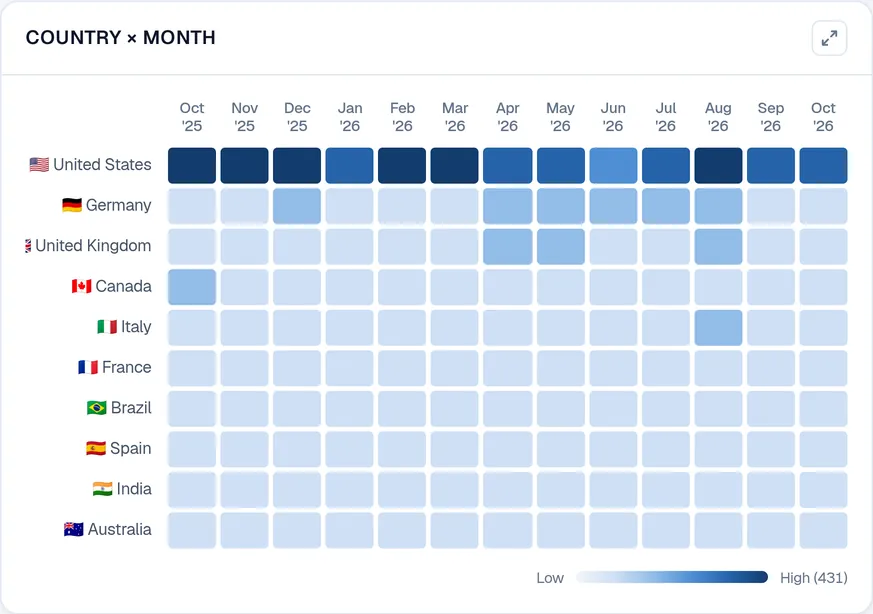
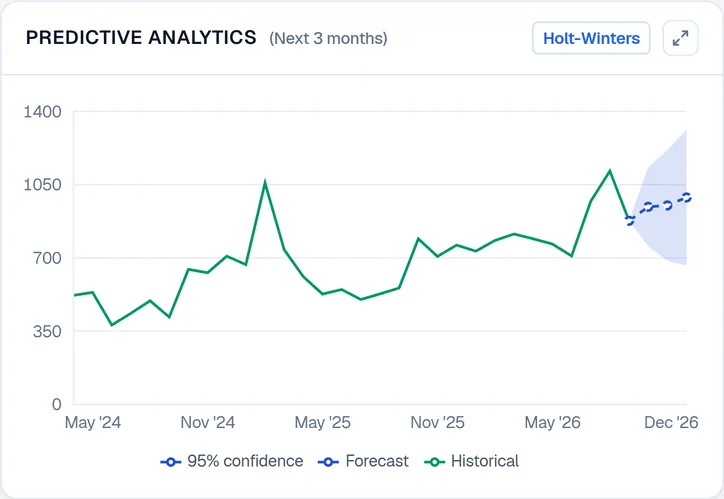
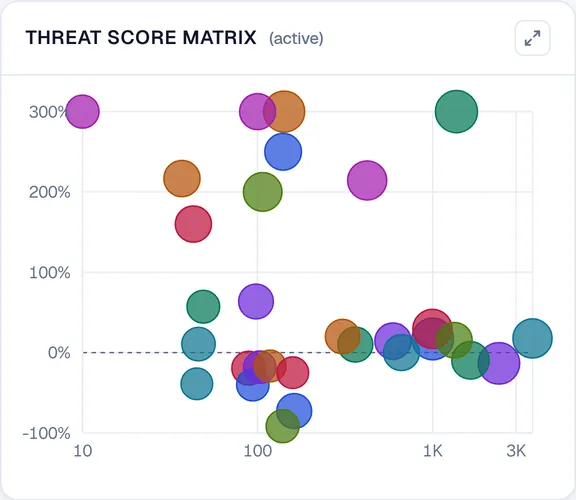
Action plan
What to fix next, mapped to the frameworks you report against.
Defensive controls are ranked by how much of the threat to your industry they block, using every attack we have recorded on organisations like yours. The gaps line up against NIST SP 800-53, NIST CSF, ISO 27001, SOC 2 and the DPDP Act.
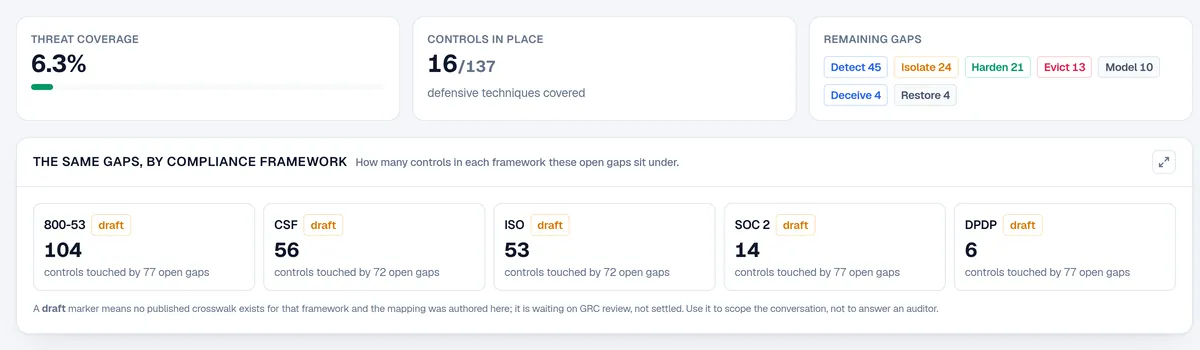
Adversary techniques
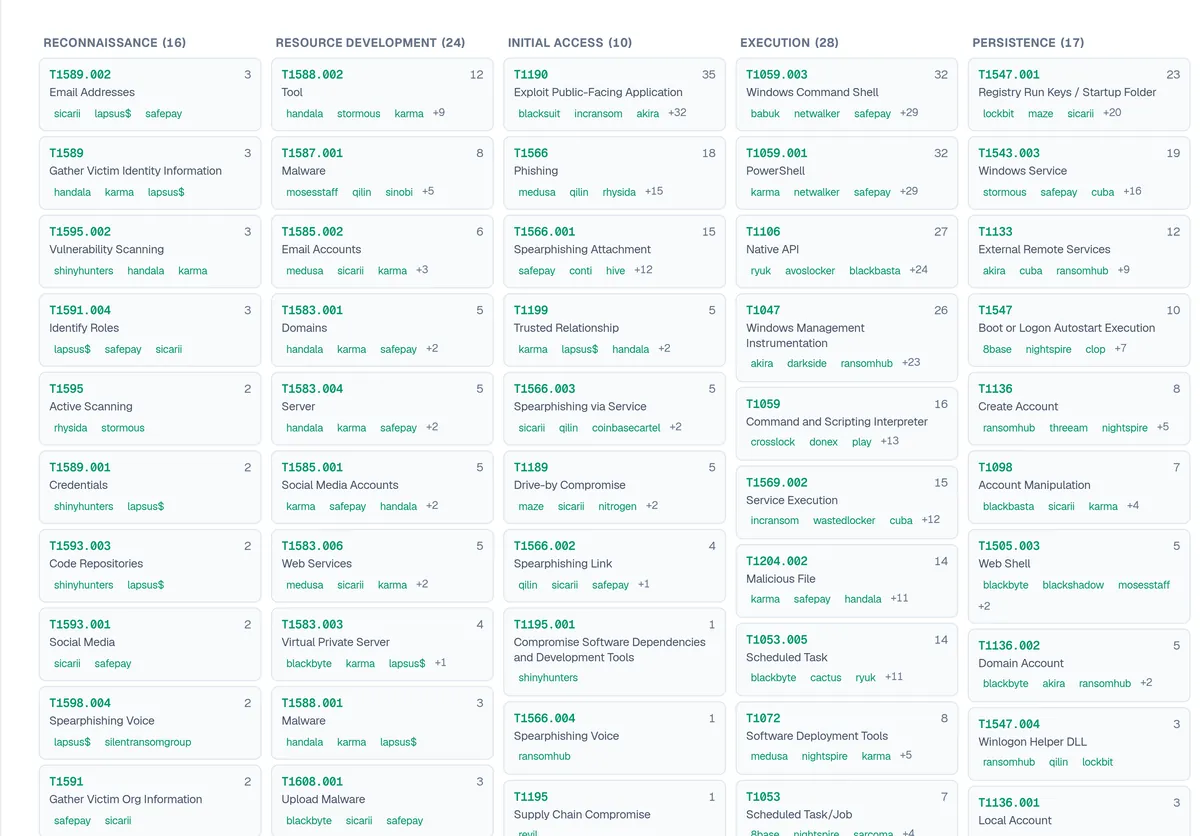
Every technique, mapped.
358 MITRE ATT&CK techniques mapped across 80 ransomware groups, alongside MITRE D3FEND countermeasures and sector playbooks.
Threat groups
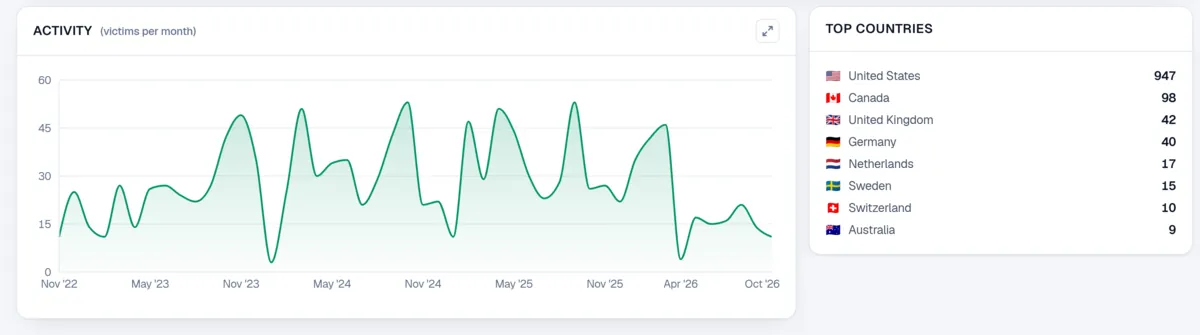
A dossier on the groups that matter.
Victims, recent activity, trend, countries and sectors hit, leak sites and a threat score for each group. Know who you are dealing with before they reach you.
Capabilities
What the platform watches for you.
-
Global view
The full dataset across every sector and region, always available. Your own view is set up once and becomes your landing page. One toggle switches between the two.
-
Ransomware tracking
542 families and 3,883 leak-site links, updated continuously. See who is hitting your sector. Groups are flagged when their activity against your sector is statistically above normal.
-
Dark web and Telegram
Your domains, brands and IP ranges matched against every post. Alerted on every match.
-
Credential exposure
7 TB+ proprietary breach corpus searched for your domains, staff and customers. Records masked at rest.
-
Exploited vulnerabilities
Your software stack checked against actively exploited CVEs, ranked by exploit likelihood.
-
Supplier exposure
Vendors checked against known breaches. Your supplier list never leaves your device.
-
CISO brief
Plain-language summary with peer benchmarking and a three-month outlook.
-
AI advisor
Ask questions about threats to your organisation in plain language. Every answer runs one read-only query and shows the query behind it.
-
Action plan
Your defensive gaps ranked, with what to fix next. Mapped to compliance frameworks.
-
Secure access
Password + authenticator, or passkey. Breach data masked at rest.
Coverage
Built on our own collection.
A live dataset. Ransomware victims in 188 countries, tracked since 2013. Our analysts watch dark web and deep web activity around the clock, so these numbers grow every week. Figures as of October 2026.
- Ransomware victims since 2013
- 33,000+
- Ransomware families
- 542
- Dark web links tracked
- 5,700+
- Forum and Telegram posts
- 52,000+
- Breach data
- 7 TB+
- Exploited CVEs scored
- 1,700+
- MITRE ATT&CK techniques
- 358
- Indian victims
- 560+
Integrations and security
Hosted in India. Plugs into your SOC.
Integrations
STIX/TAXII into your SIEM, SOAR or firewall. Real-time alerts on the dashboard and by email. Full API.
- STIX/TAXII
- SIEM
- SOAR
- Firewall
- Email alerts
- API
Security and privacy
- Client data never leaves India
- Breach data masked at rest
- Supplier list never leaves your device
- Password + authenticator, or passkey
Compliance mapping
Mapped to the DPDP Act, NIST CSF 2.0, NIST SP 800-53, ISO 27001 and SOC 2. DPDP enforcement starts May 2027.
- DPDP Act
- NIST CSF 2.0
- NIST SP 800-53
- ISO 27001
- SOC 2
Request a demo
See your own threat picture, live.
Book a demo of the platform or talk to an expert about an engagement. Under attack? Call our 24/7 line.